Cisco Meraki MS390-48UX2
Cloud Managed Switching for High-Performance Networks

End-of-Sale Notice
Cisco Meraki has announced the End-of-Sale for the MS390-48UX2 model, effective February 13, 2025 (or while supplies last).
End-of-Support date: April 4, 2032.
Recommended Replacement:
- C9300-48UN-M – 48-port of 5Gbps, UPOE, 1100wac PS, w/Meraki
Customers Note: If you currently own an MS390-48UX2 and need to renew your license, you can still purchase Enterprise License and Advanced Security License below.
Click here to jump to more pricing!
Next Steps:
- Contact Us for upgrade assistance and special pricing.
- View the C9300-48UN-M Replacement
Request Your MS390 Upgrade or License Renewal
The Cisco Meraki MS390 series is going End-of-Sale on April 4, 2032. Whether you need to renew your current license or transition to the recommended C9300 replacement, our team can guide you every step of the way.
Fill out the form below to get pricing, availability, and expert advice tailored to your network needs.
Overview:
MS390-48UX2 Highlights
- 48 x 5GbE UPoE
- 2 × 40G or 4/8 × 10G modular fiber uplinks
- Stack up to 8 units
- 480 Gbps of physical stacking
Power/PoE
- All models include a power supply
- Modular power supply/fans
- StackPower
Hardware platform
- eliable platform with 24/7 Meraki Support
- 1RU rack mountable
- Flexible mounting options
- Non-blocking switch fabric
- Email alerts for switch management
- Remote troubleshooting tools
- Manage ports from a GUI-based dashboard
- Zero-touch provisioning
- Per-port and per-client usage statistics
- Secure, user-scheduled firmware updates
Switching capabilities
- Layer 3
- OSPF Routing
- MAC forwarding entries, up to 32K
- DHCP Server, DHCP Relay
- 802.1X Authentication
- DHCP Snooping
- STP Enhancements
- IPv4 and IPv6 ACLs
- Adaptive Policy*
*Available exclusively with the Advanced License
Meraki MS390 Series Switch
The Meraki MS390 is the most powerful access switch in the Meraki portfolio which combines the simplicity of cloud-managed IT with the power of innovative Cisco switching technology. The Meraki MS390 addresses the most demanding enterprise applications by combining the simplicity of the Meraki dashboard with powerful switching hardware. To satisfy high-bandwidth applications and the deployment of high-speed 802.11ax/wifi-6 access points, the MS390 provides multigigabit ports, 480G stacking, and modular 10/40G uplinks. The MS390 delivers resiliency with fast stack convergence and StackPower. The MS390 provides Adaptive Policy using an overthe-wire tag which segments traffic into security groups to deliver scalable security. The MS390 is integrated under the Meraki dashboard to provide a simply powerful solution to the most demanding wired access applications.
Adaptive Policy provides simple & scalable security policies to segment traffic using Security Groups. Security Groups are created in the dashboard using natural language such as “IOT device” & “Guest.” The security policy intent (e.g., Permit or Deny) is then simply provisioned between Security Groups which results in the segmentation of each group’s traffic. By making security policy management intuitive and scalable relative to legacy IP-address based Access Control Lists, Adaptive Policy empowers operators to confidently secure their network traffic independent of future network changes.
By pooling & distributing power across MS390s using a series of StackPower cables, StackPower provides simple and resilient power distribution across the stack.
Simple & Powerful
Meraki access and aggregation layer switches power networks of every size. They combine secure, scalable, robust performance with an intuitive management experience that requires no additional training.
Deploy, Manage, and Troubleshoot in minutes
Meraki switches offer zero-touch provisioning and can be configured entirely from a web browser. Pioneering network topology and remote packet capture features simplify troubleshooting, especially on remote locations.
Build High-Performance, Resilient Networks
Meraki switches provide the essentials for building high-performance networks that can help maintain seamless network service. Multigigabit Ethernet squeezes more speed out of existing cabling. Switches can be physically stacked via dedicated lightning-fast cabling and cross-stack link aggregation used to create a resilient connection to the network core using all available bandwidth. Further strengthen the network with IP gateway redundancy or powerful dynamic routing using OSPF.
Build high-performance, scalable, and resilient networks with
Virtual Stacking

Configure thousands of ports simultaneously, regardless of the physical location of switches using the dashboard
Multicast Routing

Configure multicast routing on Meraki switches in minutes to eliminate traffic redundancy and improve network efficiency
APIs

Use the Dashboard API to automatically provision thousands of new sites, make bulk changes, etc. using scripts and so much more
Features:
Purpose - built Cisco technology
Use purpose built Cisco technology on the MS390 series of switches to deliver intent-based networking at scale.
Improved Physical Stacking
Improved physical stacking reduces latency to less than 1 second for faster stack convergence in case of a switch failure which is critical for enterprise deployments.
Adaptive Policy
Software feature exclusively on the MS390 to provide an additional layer of security based on the intent of the user, device, and application.
SecureConnect
SecureConnect enables to detect and verify that the MR connected to a port belongs to the same organization and then automatically configure it.
Multigigabit Ethernet
Provide the higher performance demanded by the latest access points over existing cabling.
Virtual Stacking
Simultaneously configure thousands of ports across standalone and physically stacked switches, regardless of location.
Layer 7 Visibility
Meraki switches make it easy to understand how valuable network resources are being used.
Layer 3 Scalability
Build large, resilient networks using dynamic routing protocols and warm spare technology.
Voice & Video QoS
Give latency sensitive applications the priority and bandwidth they deserve with configurable QoS.
Network Topology
View the network in real-time, showing devices and their connections and even monitor network-wide health.
Remote Live Tools
Powerful tools for identifying and correcting issues, even from thousands of miles away.
Enterprise Security
Protect the wired network from both external and internal threats.
MS Cloud Managed Switches Solutions:
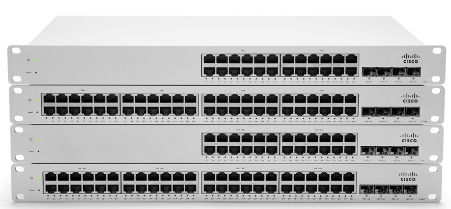
MS Cloud Managed Switches
The Cisco Meraki MS is the world's first cloud-managed switch, bringing the benefits of the cloud to enterprise networks: simplified management, reduced complexity, network wide visibility and control, and lower cost for branch and campus deployments.
Cisco Meraki access switching is available in two product lines — the MS220 and MS320 families. Mission-critical features — like deep, Layer 7 application visibility, virtual stacking, QoS for business critical applications, 802.1X access control, and more — are present in both families.
The MS320 is the flagship Cisco Meraki layer 3 access switch, designed for high-speed connectivity and high availability, with optional redundant power supplies. In addition, the MS320's full-PoE models are ideal for next generation 802.11ac wireless AP, including the Cisco Meraki MR34 — with plenty of budget to spare for other PoE clients.
The MS220 family provide layer 2 access switching, is ideal for deploying to branch locations, and supports an optional, rack-mountable remote PSU.
Inside the Meraki MS
MS220-48LP shown, features vary by model
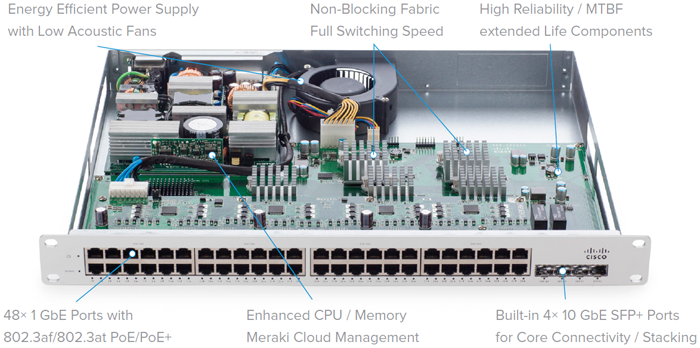
Cisco Meraki switches feature high-end hardware without the high-end price, including:
- Four built-in small form-factor pluggable transceivers (SFP / SFP+), two transceivers for MS220-8/P
- GbE and 10 GbE uplink ports for high-speed connectivity to aggregation layer switches or other upstream devices
- Wire-speed switch fabric (up to 176 Gbps) and QoS queues per port for converged voice, video, and data deployments
- Low power consumption, quiet acoustic designs, and shallow rack depth, which enable flexible deployment in wiring closets as well as offices and classrooms
- Fanless design on select models
- Up to 740 watt PoE budget with PoE+ support for powering APs, phones, cameras, and other PoE enabled devices (124W for MS220-8/P)
- Lifetime hardware warranty and advanced replacement at no additional cost
- Field-replaceable, hot-swappable power supplies and RPS option for mission-critical applications
Full Enterprise Feature Set
Cisco Meraki switches include all of the traditional Ethernet features found on the highest end products, including:
- Quality-of-Service (QoS) to prioritize mission critical traffic such as voice and video
- IEEE 802.1X support for port based network access control
- MAC-based RADIUS auth and MAC whitelisting
- Voice VLAN support for simplified VoIP deployments
- Port Mirroring to monitor network traffic
- DHCP snooping to prevent users from adding unauthorized DHCP servers on the network
- IGMP Snooping to optimize network performance with multicast traffic
- Link Aggregation Control Protocol (LACP) for high-capacity trunking, stacking, and increased availability
- Broadcast storm protection, spanning tree, BPDU guard, root guard, and other safeguards to guard against misconfigurations and reduce convergence time
- Per port VLAN configuration
- Multiple administrative roles with sophisticated security policy management
- Layer 3 on MS320 series extends routing down to the network edge
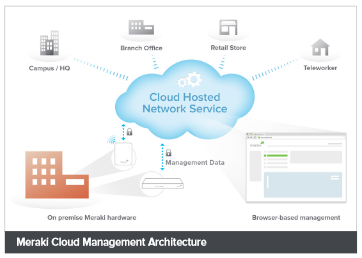
Cisco Meraki Cloud Management Architecture
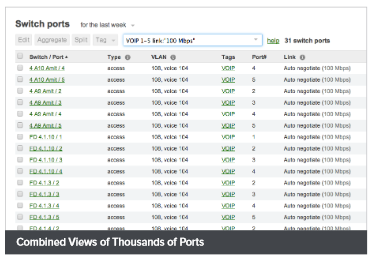
Combined Views of Thousands of Ports
Scheduled Firmware Updates
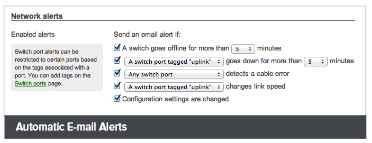
Automatic E-mail Alerts
Simplified Management and Operations
Cisco Meraki's cloud managed architecture makes it simpler than ever to quickly provision and reconfigure switch ports with security, QoS, and other parameters. The Cisco Meraki dashboard provides unified policies, event logs, and monitoring, which make it easy to manage and grow large network deployments.
By providing a complete, powerful set of management functions over the web, Cisco Meraki's cloud-based management eliminates the need for proprietary command line configuration interfaces which require expensive and time consuming certifications. Cisco Meraki MS switches can be fully deployed and provisioned in minutes, without requiring any local configuration or staging. Additional or replacement switches can be sent to remote offices and installed by non-technical staff, saving thousands of dollars in time and travel expenses.
The Cisco Meraki MS family also includes several remote diagnostic features, from network connectivity and cable integrity tests to latency measurement tools. For deep client troubleshooting, administrators can even perform per-port remote pcap packet captures without any additional probes or hardware on site.
Layer 7 Visibility
Cisco Meraki is the only switch to include integrated Layer 7 fingerprinting. Identify hundreds of applications from business apps to BitTorrent and YouTube. User fingerprinting with Google-like search allows administrators to easily identify and control individual users, PCs, iMacs, iPads, Androids, and other devices. This unprecedented visibility allows you to optimize network resources and maintain optimal network performance.
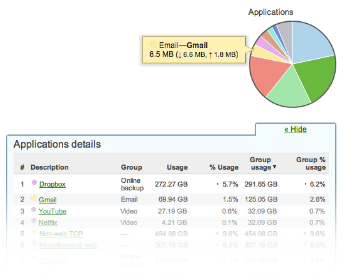
Applications details
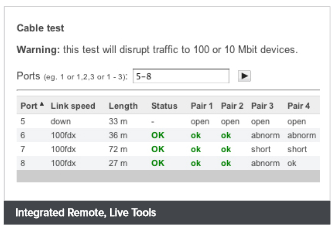
Integrated Remote, Live Tools
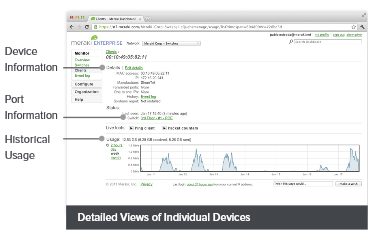
Detailed Views of Individual Devices
Converged Voice, Video and Data Environments
The Cisco Meraki switch family is designed to unify data, voice, and video onto a single IP backbone. All Cisco Meraki switches support rich quality- of-service (QoS) functionality for prioritizing data, voice, and video traffic. The switches support eight class-of-service (CoS) queues on every port, enabling them to maintain end-to-end traffic prioritization.
PoE models provide 15.4 watts of power per port for VoIP telephones, IP security cameras, wireless access points (APs), and other IP devices. The Cisco Meraki MS switches also support standards-based 25.5 watt (30 watt max per port) IEEE 802.3at for powering networked devices like multiple radio IEEE 802.11n APs and video phones that may require more power than available with IEEE 802.3af. In addition, using LLDP, PoE power is intelligently budgeted to maximize the number of PoE clients supported.
To ease deployment, Cisco Meraki switches support the industry- standard Link Layer Discovery Protocol (LLDP), enabling switches to automatically discover Ethernet-enabled devices, determine their power requirements and join the correct virtual LAN (VLAN).
Cisco Meraki's Unified Software Architecture
Cisco Meraki switches run the same Cisco Meraki operating system used by Cisco Meraki's firewalls and wireless LAN products. The use of a common operating system allows Cisco Meraki to deliver a consistent experience across all product lines
Layer 3
Cisco Meraki MS320 series switches augment security and performance with built-in layer 3 benefits. Large network deployments can create scalable network architecutres and manage routing between VLANs through Cisco Meraki's intuitive, web-based dashboard.
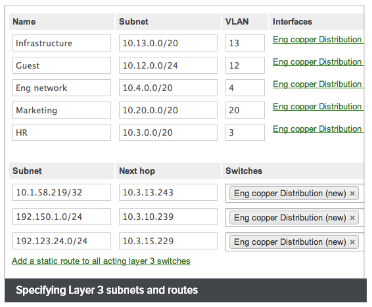
Specifying Layer 3 subnets and routes
Designed for Reliability & Environmental Efficiency
The Cisco Meraki switch family was designed for reliable, long-lived operation in wiring closet environments, which may be prone to high temperatures and limited ventilation. By minimizing total component count and only using proven switching silicon, Cisco Meraki is able to deliver mean time between failure (MTBF) ratings of over 750,000 hours on products such as the Cisco Meraki MS220-8.
Each Cisco Meraki switch also operates with a split-plane architecture, where silicon-based switching and data forwarding are separated from software-based control and management. By decoupling the underlying switching logic from control, each unit is able to deliver wire-speed switching even when advanced software features such as Layer 7 host and OS fingerprinting are enabled.
Finally, the highly integrated designs of Cisco Meraki switches result in power and cooling savings in large deployment environments of 30- 60% when compared with similar managed Gigabit switches.
Cisco Meraki's cloud-based system makes it easy to manage a single switch, or thousands of distributed switches, from a single interface.
- Troubleshoot problems remotely, e.g., find which port has a bad cable attached.
- Add or replace switches without having to send a technician onsite. Switches automatically download their current configuration as soon as they are connected to the network.
- Receive email alerts or SMS messages whenever there's a problem at a remote site.1
MS switches are ideal for small and large scale campus deployments, where reliability, scalability, and managability are top priorities.
- Virtual Stacking lets administators manage up to tens of thousands of ports in a single interface without having to physically connect stack members.
- 10GbE cable SFP+ ports with link aggregation provide high speed connectivity to aggregation switches such as the MS420.
- Get alerts when any switch fails or goes offline, before users complain.
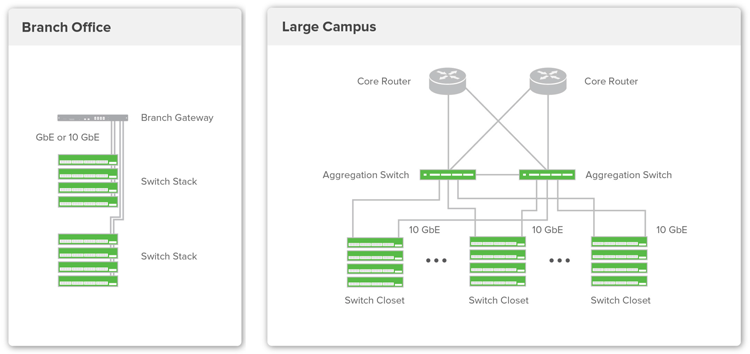
Cloud Management:
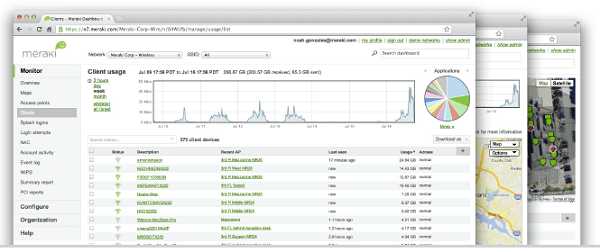
Cisco Meraki's cloud based management provides centralized visibility & control over Cisco Meraki's wired & wireless networking hardware, without the cost and complexity of wireless controllers or overlay management systems. Integrated with Cisco Meraki's entire product portfolio, cloud management provides feature rich, scalable, and intuitive centralized management for networks of any size.
Highlights
- Unified visibility and control of the entire network via a single dashboard: wireless, switching, and security appliances
- Streamlines large networks with tens of thousands of endpoints
- Zero-touch provisioning for rapid deployment
- Built-in multi site network management tools
- Automated network monitoring and alerts
- Intuitive interface eliminates costly training or added staff
- Network tagging engine - search and sync settings by tag
- Role-based administration and auditable change logs
- Continuous feature updates delivered from the cloud
- Highly available and secure (PCI / HIPAA compliant)
Cloud Managed Networks
Cisco Meraki's hardware products are built from the ground up for cloud management. As a result, they come out of the box with centralized control, layer 7 device and application visibility, real time web-based diagnostics, monitoring, reporting, and much more.
Cisco Meraki networks deploy quickly and easily, without training or dedicated staff. Moreover, Cisco Meraki provides a rich feature set that provides complete control over devices, users, and applications, allowing for flexible access policies and rich security without added cost or complexity.
Cisco Meraki's cloud management provides the features, security, and scalability for networks of any size. Cisco Meraki scales from small sites to campuses, and even distributed networks with thousands of sites. Cisco Meraki devices, which self-provision via the cloud, can be deployed in branches without IT. Firmware and security signature updates are delivered seamlessly, over the web. With the cloud, branches can automatically establish secure VPN tunnels between one another with a single click.
With a secure, PCI and HIPAA compliant architecture and fault tolerant design that preserves local network functionality during WAN outages, Cisco Meraki is field proven in high security and mission critical network applications.
Cloud Management Architecture
Cisco Meraki's architecture provides feature rich network management without on-site management appliances or WiFi controllers.
Every Cisco Meraki device - including wirelesss access points, Ethernet switches, and security appliances - connects over the Internet to Cisco Meraki's datacenters, which run Cisco Meraki's cloud management platform. These connections, secured via SSL, utilize a patented protocol that provides real time visibility and control, yet uses minimal bandwidth overhead (typically 1 kbps or less.)
In place of traditional command-line based network configuration, Cisco Meraki provides a rich web based dashboard, providing visibility and control over up to tens of thousands of Cisco Meraki devices, anywhere in the world. Tools, designed to scale to large and distributed networks, make policy changes, firmware updates, deploying new branches, etc. simple and expedient, regardless of size or location. Cisco Meraki's real time protocols combine the immediacy of on-premise management applications with the simplicity and centralized control of a cloud application.
Every Cisco Meraki device is engineered for cloud management. Specifically, this means that Cisco Meraki devices are designed with memory and CPU resources to perform packet processing, QoS, layer 3-7 security, encryption, etc. at the network edge. As a result, no network traffic passes through the cloud, with the cloud providing management functionality out of the data path. This architecture enables networks to scale horizontally, adding capacity simply by adding more endpoints, without concern for centralized bottlenecks or chokepoints. Equally important, since all packet processing is performed on premise, end-user functionality is not compromised if the network's connection to the cloud is interrupted.
Cisco Meraki's cloud platform is designed to spread computation and storage across independent server clusters in geographically isolated datacenters. Any server or datacenter can fail without affecting customers or the rest of the system. Additionally, Cisco Meraki's datacenter design is field proven to support tens of thousands of endpoints.
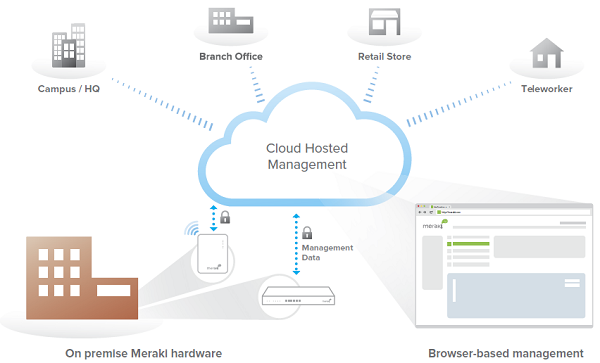
Cloud Management Architecture
Powerful Insight and Troubleshooting Tools
Cisco Meraki's cloud architecture delivers powerful insight and includes live tools integrated directly into the dashboard, giving instant analysis of performance, connectivity, and more. Using live tools, network administrators no longer need to go on site to perform routine troubleshooting tests. Visibility into devices, users, and applications gives administrators the information needed to enforce security policies and enable the performance needed in today's demanding network environments.
Troubleshooting tools such as ping, traceroute, throughput, and even live packet captures are integrated directly into the Cisco Meraki dashboard, dramatically reducing resolution times and enabling troubleshooting at remote locations without on-site IT staff.
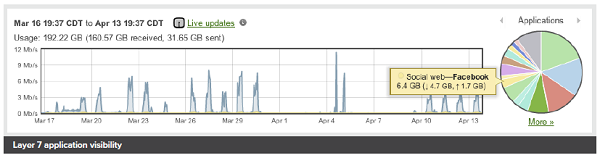
Layer 7 application visibility
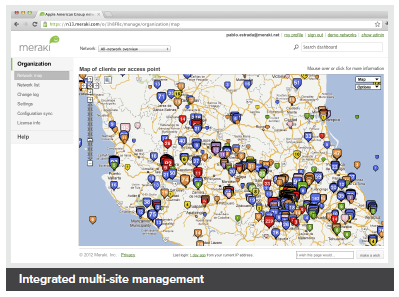
Integrated multi-site management
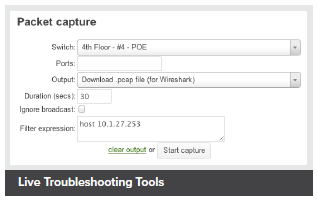
Live Troubleshooting Tools
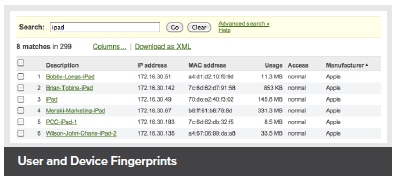
User and Device Fingerprints
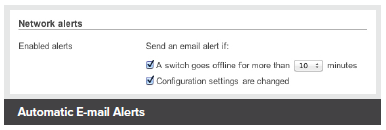
Automatic E-mail Alerts
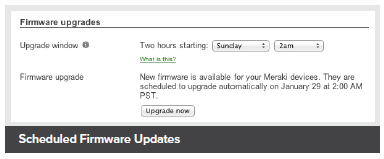
Scheduled Firmware Updates
Out-of-Band Control Plane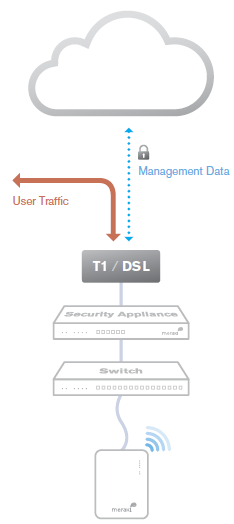
Cisco Meraki's out-of-band control plane separates network management data from user data. Management data (e.g., configuration, statistics, monitoring, etc.) flows from Cisco Meraki devices (wireless access points, switches, and security appliances) to Cisco Meraki's cloud over a secure Internet connection. User data (web browsing, internal applications, etc.) does not flow through the cloud, instead flowing directly to its destination on the LAN or across the WAN.
Advantages of an out of band control plane:
Scalability
- Unlimited throughput: no centralized controller bottlenecks
- Add devices or sites without MPLS tunnels
- Add switching capacity without stacking limitations
Reliability
- Redundant cloud service provides high availability
- Network functions even if management traffic is interrupted
Security
- No user traffic passes through Cisco Meraki's datacenters
- Fully HIPAA / PCI compliant
What happens if a network loses connectivity to the Cisco Meraki cloud?
Because of Cisco Meraki's out of band architecture, most end users are not affected if Cisco Meraki wireless APs, switches, or security appliances cannot communicate with Cisco Meraki's cloud services (e.g., because of a temporary WAN failure):
- Users can access the local network (printers, file shares, etc.)
- If WAN connectivity is available, users can access the Internet
- Network policies (firewall rules, QoS, etc.) continue to be enforced
- Users can authenticate via 802.1X/RADIUS and can roam wirelessly between access points
- Users can initiate and renew DHCP leases
- Established VPN tunnels continue to operate
- Local configuration tools are available (e.g., device IP configuration)
While Cisco Meraki's cloud is unreachable, management, monitoring, and hosted services are temporarily unavailable:
- Configuration and diagnostic tools are unavailable
- Usage statistics are stored locally until the connection to the cloud is re-established, at which time they are pushed to the cloud
- Splash pages and related functionality are unavailable
Cisco Meraki Datacenter Design
Cisco Meraki's cloud management service is colocated in tier-1, SAS70 type II certified datacenters. These datacenters feature state of the art physical and cyber security and highly reliable designs. All Cisco Meraki services are replicated across multiple independent datacenters, so that customer-facing services fail over rapidly in the event of a catastrophic datacenter failure.
- Five geographically dispersed datacenters
- Every customer's data (network configuration and usage metrics) replicated across three independent datacenters
- Real-time data replication between datacenters (within 60 seconds)
- Nightly archival backups
Availability Monitoring
- 24x7 automated failure detection — all servers are tested every five minutes from multiple locations
- Rapid escalation procedures across multiple operations teams
- Independent outage alert system with 3x redundancy
Disaster Recovery
- Rapid failover to hot spare in event of hardware failure or natural disaster
- Out of band architecture preserves end-user network functionality, even if connectivity to Cisco Meraki's cloud services is interrupted
- Failover procedures drilled weekly
Cloud Services Security
- 24x7 automated intrusion detection
- Protected via IP and port-based firewalls
- Access restricted by IP address and verified by public key (RSA)
- Systems are not accessible via password access
- Administrators automatically alerted on configuration changes
Physical Security
- High security card keys and biometric readers control facility access
- All entries, exits, and cabinets are monitored by video surveillance
- Security guards monitor all traffic into and out of the datacenters 24x7, ensuring that entry processes are followed
- Only configuration and usage statistics are stored in the cloud
- End user data does not traverse through the datacenter
- All sensitive data (e.g., passwords) stored in encrypted format
Disaster Preparedness
- Datacenters feature sophisticated sprinkler systems with interlocks to prevent accidental water discharge
- Diesel generators provide backup power in the event of power loss
- UPS systems condition power and ensure orderly shutdown in the event of a full power outage
- Each datacenter has service from at least two top-tier carriers
- Seismic bracing for raised floor, cabinets, and support systems
- In the event of a catastrophic datacenter failure, services fail over to another geographically separate datacenter
Environmental Controls
- Over-provisioned HVAC systems provide cooling and humidity control
- Flooring systems are dedicated for air distribution
Certification
- Cisco Meraki datacenters are SAS70 type II certified
- PCI level 1 certified
Service Level Agreement
- Cisco Meraki's cloud management is backed by a 99.99% uptime SLA. See www.Cisco Meraki.com/trust for details.
Security Tools for Administrators
In addition to Cisco Meraki's secure out-of-band architecture and hardened datacenters, Cisco Meraki provides a number of tools for administrators to maximize the security of their network deployments. These tools provide optimal protection, visibility, and control over your Cisco Meraki network.
Two-factor authentication
Two-factor authentication adds an extra layer of security to an organization's network by requiring access to an administrator's phone, in addition to her username and password, in order to log in to Cisco Meraki's cloud services. Cisco Meraki's two factor authentication implementation uses secure, convenient, and cost effective SMS technology: after entering their username and password, an administrator is sent an a one-time passcode via SMS, which they must enter before authentication is complete. In the event that a hacker guesses or learns an administrator's password, she still will not be able to access the organization's account, as the hacker does not have the administrator's phone. Cisco Meraki includes two-factor authentication for all enterprise users at no additional cost.Password policies
Organization-wide security policies for Cisco Meraki accounts help protect access to the Cisco Meraki dashboard. These tools allow administrators to:
- Force periodic password changes (e.g., every 90 days)
- Require minimum password length and complexity
- Lock users out after repeated failed login attempts
- Disallow password reuse
- Restrict logins by IP address
Role-based administration
Role-based administration lets supervisors appoint administrators for specific subsets of an organization, and specify whether they have read-only access to reports and troubleshooting tools, administer managed guest access, or can make configuration changes to the network. This minimizes the chance of accidental or malicious misconfiguration, and restricts errors to isolated parts of the network.Configuration change alerts
The Cisco Meraki system can automatically send human-readable email and text message alerts when configuration changes are made, enabling the entire IT organization to stay abreast of new policies. Change alerts are particularly important with large or distributed IT organizations.Configuration and login audits
Cisco Meraki logs the time, IP, and approximate location (city, state) of logged in administrators. A searchable configuration change log indicates what configuration changes were made, who they were made by, and which part of the organization the change occurred in.SSL certificates
Cisco Meraki accounts can only be accessed via https, ensuring that all communication between an administrator's browser and Cisco Meraki's cloud services is encrypted.Idle Timeout
30 seconds before being logged out, users are shown a notice that allows them to extend their session. Once time expires, users are asked to log in again.
Specifications:
| Specifications | |
|---|---|
| Interfaces |
|
| Management |
|
| Remote Diagnostics |
|
| Remote Packet Capture |
|
| Scalable Stacking |
|
| Ethernet Switching Capabilities |
|
| Security |
|
| Adaptive Policy |
|
| SecureConnect |
|
| Performance |
|
| Layer 3 Capabilities |
|
| Power |
|
| Mounting |
|
| Environment |
|
| Regulatory |
|
| Safety Compliance |
|
| Warranty |
|
| MTBF (at 25°C) |
|
| Physical Specifications (H × W × D) |
|
Accessories:
Optics
The Cisco Meraki MS support pluggable optics for high-speed connectivity. Cisco Meraki offers several standards-based Gigabit and 10 Gigabit pluggable modules
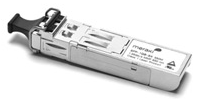
1 GbE SFP SX Fiber Transceiver
1 GbE SFP LX Fiber Transceiver
10 GbE SFP+ Short Range Fiber Transceiver
10 GbE SFP+ LR Fiber Transceiver
10 GbE SFP+ LRM Fiber Transceiver

40 GbE QSFP+ SR4 Fiber Transceiver
40 GbE QSFP+ LR4 Fiber Transceiver
40 GbE QSFP+ CSR4 Fiber Transceiver
40 GbE QSFP+ SR-BD Fiber Transceiver
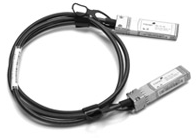
Twinax Cable with SFP+ Connectors
Twinax Cable with SFP+ Connectors (3m)
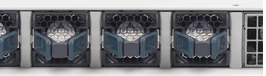
16K2 System Fan

120G Stacking Cable (0.5m)
120G Stacking Cable (1m)
120G Stacking Cable (3m)

StackPower Cable (30cm)
StackPower Cable (150cm)

2 x 40G Uplink Module

4 x 10G Uplink Module

8 x 10G Uplink Module
| Accessory | Description | Supported Models |
| MA-SFP-1GB-SX | Cisco Meraki 1 GbE SFP SX Multi-Mode Fiber Module | MS220/320/350/390/420 Family |
| MA-SFP-1GB-LX10 | Cisco Meraki 1 GbE SFP LX10 Single-Mode Fiber Module | MS220/320/350/390/420 Family |
| MA-SFP-10GB-SR | Cisco Meraki 10 GbE SFP+ SR Multi-Mode Fiber Module | MS320/350/390/420 Family |
| MA-SFP-10GB-LRM | Cisco Meraki 10GbE SFP+ LRM Multi-Mode Fiber Module | MS320/350/390/420 Family |
| MA-SFP-10GB-LR | Cisco Meraki 10 GbE SFP+ LR Single-Mode Fiber Module | MS320/350/390/420 Family |
| MA-CBL-TA-1M | Cisco Meraki 10 GbE Twinax Cable with SFP+ Connectors | MS320/350/390/420 Family |
| MA-CBL-120G-50CM | Cisco Meraki 120G Stacking Cable, 0.5 Meter | All Models |
| MA-CBL-120G-1M | Cisco Meraki 120G Stacking Cable, 1 Meter | All Models |
| MA-CBL-120G-3M | Cisco Meraki 120G Stacking Cable, 3 Meter | All Models |
| MA-CBL-SPWR-30CM | Cisco Meraki MS390 30CM StackPower Cable | All Models |
| MA-CBL-SPWR-150CM | Cisco Meraki MS390 150CM StackPower Cable | All Models |
| MA-FAN-16K2 | System Fan | All Models |
| MA-MOD-2X40G | 2 x 40G Uplink Module | All Models |
| MA-MOD-4X10G | 4 x 10G Uplink Module | All Models |
| MA-MOD-8X10G | 8 x 10G Uplink Module | All Models |
Power Options
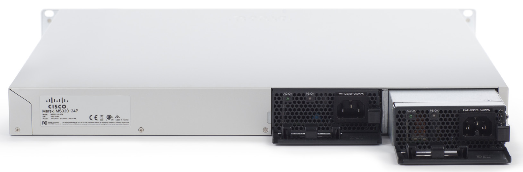
Back end of MS390 shown, highlighting redundant power supplies

350 Watt AC Power Supply
715 Watt AC Power Supply

1100 Watt AC Power Supply
| Accessory | Description | Supported Models |
| MA-PWR-350WAC | Cisco Meraki 350W AC Power Supply | MS390-24-HW, MS390-48-HW |
| MA-PWR-715WAC | Cisco Meraki 715W AC Power Supply | All Models |
| MA-PWR-1100WAC | Cisco Meraki 1100W AC Power Supply | All Models |
Documentation:
Download the Cisco Meraki MS390 Datasheet (PDF).
Download the Cisco Meraki Cloud Management Datasheet (PDF).
Pricing Notes:
- Pricing and product availability subject to change without notice.
List Price:
Our Price: $661.81
List Price:
Our Price: $1,489.34
List Price:
Our Price: $2,482.06
List Price:
Our Price: $3,474.77
List Price:
Our Price: $6,758.32
List Price:
Our Price: $1,552.21
List Price:
Our Price: $3,492.35
List Price:
Our Price: $5,820.95
List Price:
Our Price: $8,149.01